Agent 365 Exception Register Review for Security Leads
An agent with broad permissions and an expired approval creates a business liability nobody clearly owns. I recommend an Agent 365 governance exception register review when your inventory shows what exists, but cannot explain why risky access remains acceptable.
The commercial exposure includes data leakage, audit findings, difficult insurance renewals, and productivity loss when an unmanaged dependency fails. A useful review ends with documented decisions, accountable owners, and evidence that approved restrictions work.
Start by separating the agent inventory from the decisions your security team needs to defend.
Key Takeaways
- Agent 365 provides governance and control for agents, while Copilot Studio, Microsoft Foundry, custom applications, and third-party platforms run them.
- Keep the agent inventory separate from the exception register. Each exception needs an accountable owner, business justification, safeguards, expiration date, and evidence that restrictions work.
- Review agent identities, permissions, data paths, monitoring, and recovery dependencies. Registry presence alone doesn't prove approval or effective protection.
- Roll out governance in stages, and assess licensing against your existing E3, E5, or E5 plus Copilot baseline before choosing a broader engagement.
Where Agent 365 Governance Fits the Review
Agent 365 is Microsoft's unified control plane for discovering, governing, securing, and managing AI agents. It isn't an agent runtime. Copilot Studio, Microsoft Foundry, custom applications, and third-party platforms still execute the workloads.
Microsoft announced general availability on May 1, 2026. That announcement separately labeled enhanced shadow-agent discovery and management capabilities as preview. I distinguish GA controls from preview-dependent coverage in the review evidence rather than treating the whole platform as uniformly mature.
Identity establishes accountability
Microsoft Entra Agent ID provides an agent identity with lifecycle management, conditional access, and audit trails. The review connects each identity to a business owner, sponsor, purpose, and retirement decision.
Least privilege and role-based access control should limit what each agent can reach, with time-limited access packages. Delegated access and autonomous permissions require separate examination because their exposure differs.
Security and data controls need evidence
Microsoft Defender provides runtime threat detection and security alerts. The response plan should identify supported ways to quarantine or block suspicious agents, revoke permissions, and notify security teams.
Microsoft Purview provides DLP, sensitivity, retention, and information-barrier controls across supported workloads. I assess actual coverage, including external connectors, rather than accepting policy configuration as proof of enforcement.
Microsoft's Agent 365 service description separates basic administration from advanced capabilities requiring Agent 365 or an applicable bundle.
What the Exception Register Review Assesses
Keep the exception register in your existing risk or ticketing system, linked to identifiers in the Agent 365 agent registry. The inventory records agents; the exception register records approved departures from your security standard.
Scope follows business exposure
Review explicitly registered and self-registered agents alongside discovered shadow agents deployed without approval. Discovery depends on supported integrations and telemetry, so absence from the registry doesn't prove absence from your environment.
The assessment covers agent identity, ownership, permissions, connectors, sensitive-data access, monitoring, and recovery dependencies. Include third-party agents wherever they touch business information or operational systems.
For cloud infrastructure and hybrid environments, map those dependencies beyond Microsoft 365. Endpoint security and device hardening remain relevant when local agents access files, credentials, or internal tools.
Every exception needs a defensible decision
An exception should identify the agent, affected control, business justification, accountable approver, compensating safeguards, expiration date, and evidence of closure and internal policy compliance.
Record residual risk in commercial terms. Customer-data exposure, service interruption, and lost staff time give executives a clearer decision than an unexplained technical severity score.
Registration proves that an agent appears in the inventory. It doesn't prove business approval, appropriate permissions, or effective data protection.
I recommend separating accepted risks from unresolved findings. Otherwise, an overdue remediation task can look like an authorized exception.
How the Review Runs in the Admin Center
The engagement should begin with agreed access, scope, and evidence handling. Start with a read-only assessment; production changes require separate authorization.
Microsoft documents the agent registry administration workflow. The practical review sequence is:
- Open Agent 365 > agent registry in the Microsoft 365 admin center. Capture the in-scope inventory, ownership, deployment status, and available identity references.
- Reconcile registry entries against Copilot Studio environments, enterprise applications, endpoint discoveries, approved business solutions, and permissions. Flag missing owners and unexplained discrepancies.
- Trace access and data paths through Microsoft Entra, Purview, and Defender evidence. Distinguish inherited access from permissions granted directly to the agent.
- Test the proposed restriction in a controlled context. Record allowed and blocked behavior, relevant logs, and the rollback route before closing an exception.
Copilot Studio agents register automatically, but registration doesn't replace approval. Access to Copilot Studio can also be restricted to defined security groups.
For third-party agents, I recommend a governed allowance when identity, permissions, telemetry, and response controls are adequate. Block or isolate access when those controls are missing, until the business sponsor resolves the gap.
The client should receive evidence-linked findings, not just screenshots of configuration pages.
What Security Leads Receive at the End
A review should produce artifacts your team can operate after the engagement ends. I would make the deliverables explicit in the scope of work.
A decision-ready register
The primary deliverable is a normalized exception register with disposition, owner, deadline, approval authority, and supporting evidence. Each record should distinguish remediation, temporary acceptance, withdrawal, or closure.
Alongside it, provide a prioritized remediation roadmap. Group work by dependency so your team doesn't tighten agent permissions before repairing the underlying access model.
An executive view and operating handoff
The executive summary should explain exposure, unresolved decisions, and operational consequences. It should support audit discussions, internal business compliance, and insurance documentation without promising that any particular insurer will accept it.
The handoff also needs a review cadence, escalation route, and ownership-change process. Monthly security reviews, user lifecycle changes, and policy updates should trigger exception reassessment when relevant.
For a broader assessment, my cybersecurity risk management services connect Microsoft 365 findings with endpoint protection, policies, and incident-response readiness.
Roll Out Controls Without Disrupting Useful Agents
I recommend a proportionate, three-stage governance framework: visibility without enforcement, controls for new agents, then bringing existing agents under management. This sequence reduces the risk of blocking a useful workflow before understanding its dependencies.
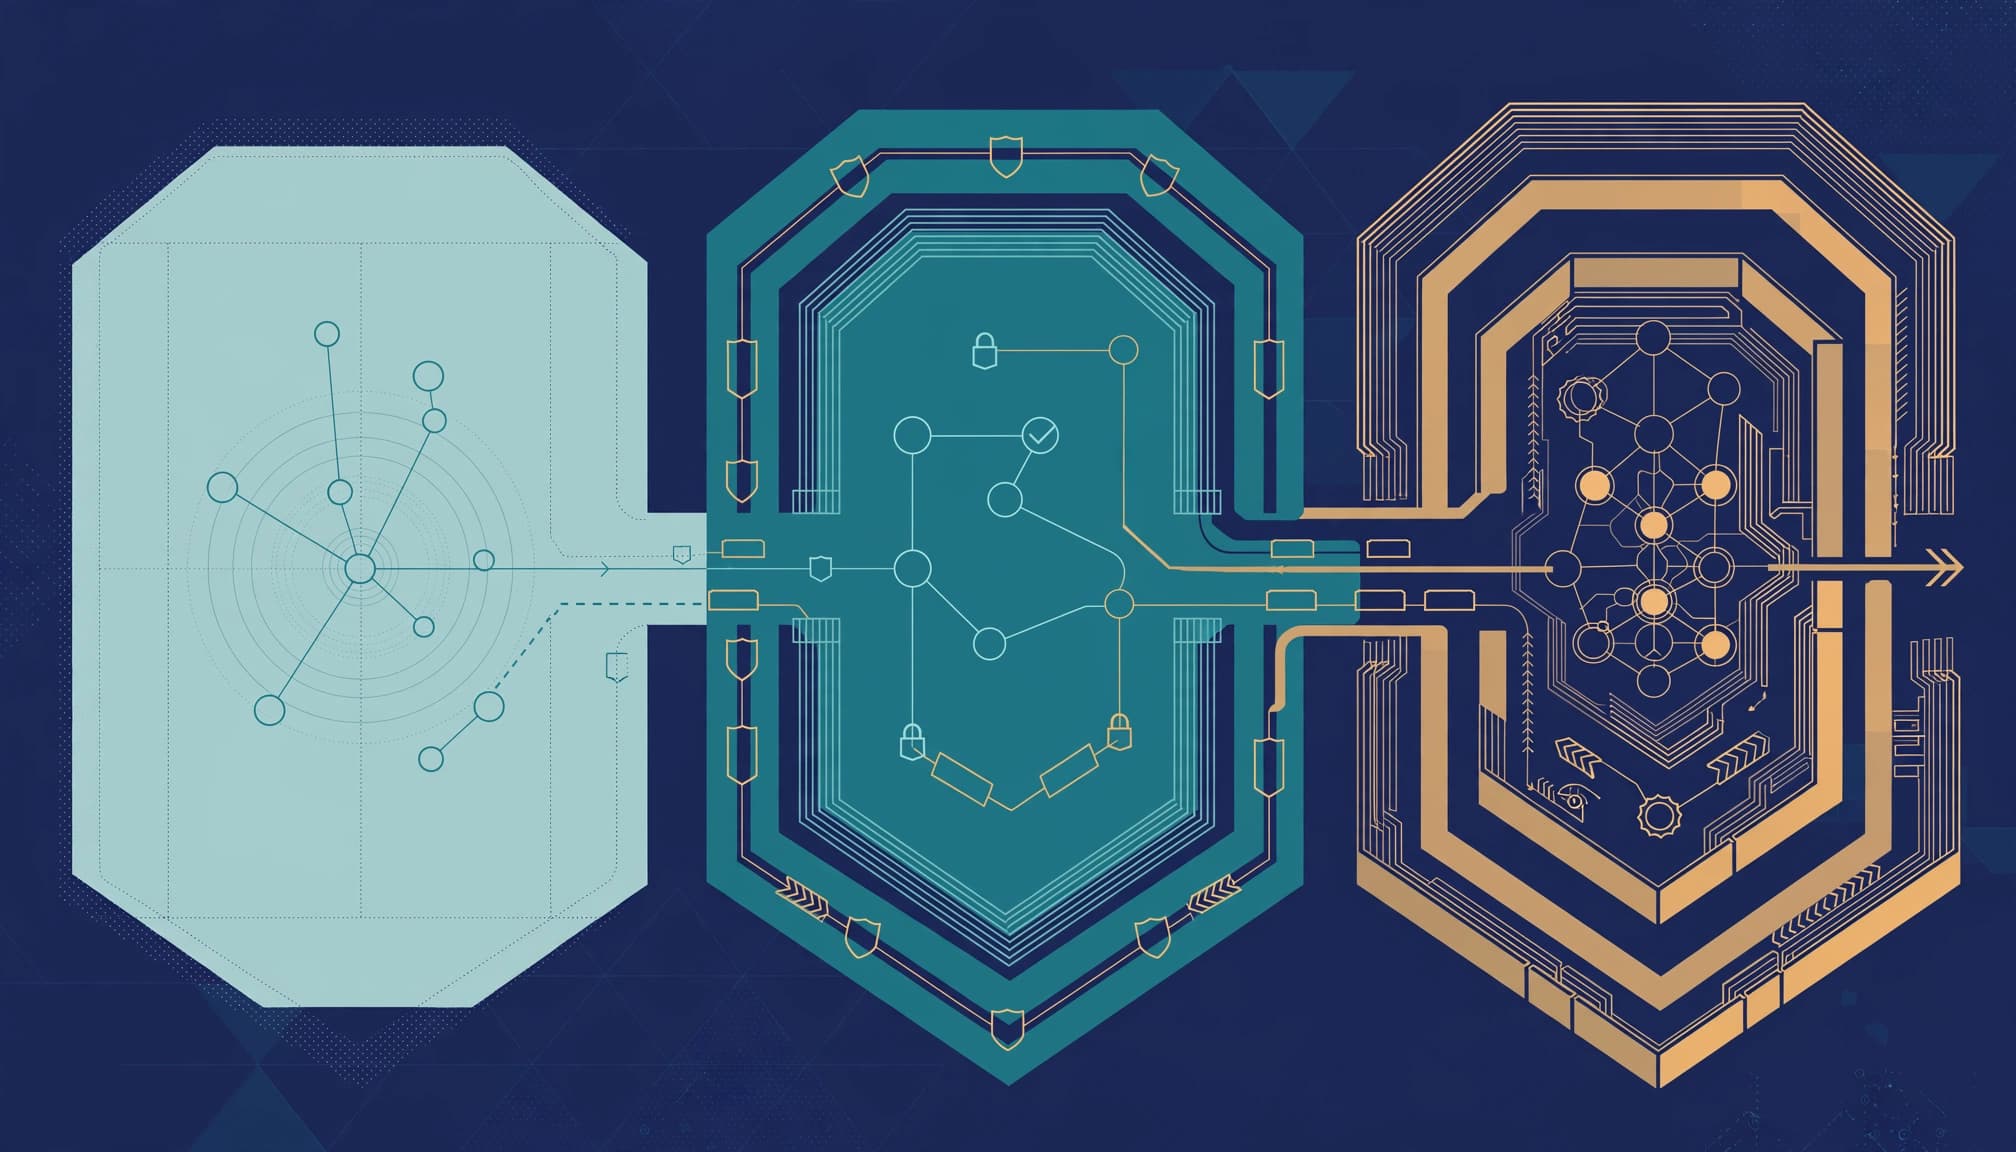
A three-zone model gives each agent a proportionate review standard.
| Zone | Business use | Governance intensity |
|---|---|---|
| Personal productivity | Individual assistance with limited access | Named owner, restricted permissions, basic monitoring |
| Team solutions | Shared departmental workflows | Approval, data review, lifecycle controls, documented exceptions |
| Business-critical agents | Revenue or operational dependencies | Formal risk acceptance, tested containment, recovery planning |
The zone should reflect permissions and business impact, not the developer's job title.
During the first stage, identify shadow agents without automatically approving them. During the second, require ownership and governance controls before new agents enter production. Finally, assign existing agents deadlines based on exposure and dependency.
Provisioning time also belongs in rollout planning. The commonly reported 10 to 15 minute agentic-user provisioning window, with possible delays up to 24 hours, is a planning estimate rather than a contractual SLA.
For business-critical agents, document a manual fallback. Governance changes should protect business continuity and security without creating avoidable downtime.
Compare Licensing Against the Existing Baseline
Microsoft lists standalone Agent 365 licensing at $15 per user per month, paid yearly. Microsoft 365 E7 costs $99 per user per month with an annual commitment.
The $99 E7 price covers licensing only. Azure compute, model, and message consumption bill separately where incurred. Agent 365 uses per-user pricing, not a per-agent runtime charge.
E3 and E5 require different comparisons
Microsoft 365 E3 and E5 don't include Agent 365 by themselves. E3-based eligibility includes additional Defender and Purview suite requirements, so adding only the standalone fee understates that baseline's cost.
For Microsoft 365 E5, the current US list-price comparison is $60 plus $15 for Agent 365, or $75 per user monthly. E7 costs $24 more and includes Microsoft 365 Copilot and Microsoft Entra Suite.
That difference needs a business case if those additional products won't be used.
E5 plus standalone Copilot changes the calculation
For an E5 plus standalone Microsoft 365 Copilot baseline, the list-price arithmetic is $60 plus $30 plus $15, totaling $105 with Agent 365.
Compared with E7 at $99, that is a $6 monthly cost difference per user. The $99 price covers licensing only, and Azure compute, model, and message consumption bill separately where incurred. Across 100 users, the difference is $600 monthly before negotiated discounts.
I compare assigned seats, actual usage, prerequisites, renewal dates, and existing discounts. Bundle value depends on the baseline and adoption, not the headline price alone.
When This Engagement Isn't Worthwhile
A dedicated review adds little value when you have few low-access agents, clear owners, current approvals, and effective internal review. A short licensing or readiness assessment is more proportionate.
It also disappoints when the main problem is poor environment hygiene. Agent 365 won't repair excessive SharePoint access, abandoned accounts, weak guest controls, or incomplete audit retention.
Past Office 365 migration decisions can leave those problems behind. Address identity management, external access, and tenant security hardening before expanding agent privileges.
If your immediate need is an incident response, contain the threat first. An exception review belongs after urgent recovery work.
I also avoid presenting this engagement as a substitute for ongoing cloud management or managed IT for small businesses. Someone still needs to operate the controls and maintain the register.
Frequently Asked Questions
Does Agent 365 replace Microsoft 365 Copilot?
No. Microsoft 365 Copilot provides user-facing assistance. Agent 365 provides governance and control over agents, including agents built outside Copilot.
Microsoft's Agent 365 overview describes the centralized management role. Neither product automatically fixes inappropriate access to underlying business data.
How should exceptions expire or close?
Set an expiration date when approving the exception. Require reassessment before renewal, particularly after ownership, connector, permission, or data changes.
Close the record only after evidence shows the agreed restriction works or the agent has been retired. If remediation remains incomplete, obtain a fresh risk decision instead of silently extending the deadline.
Start With a Bounded Readiness Assessment
An exception review is worthwhile when it turns uncertain agent access into owned, time-bound decisions. Its value comes from evidence and follow-through, not inventory size.
I recommend starting with a readiness assessment or licensing review against your current E3, E5, or E5 plus Copilot baseline. My Microsoft 365 advisory can help separate tenant security work, subscription choices, and agent governance before you commit to a larger engagement.